US Ransomware Attacks Surge 200%: New Report Reveals Alarming Threat
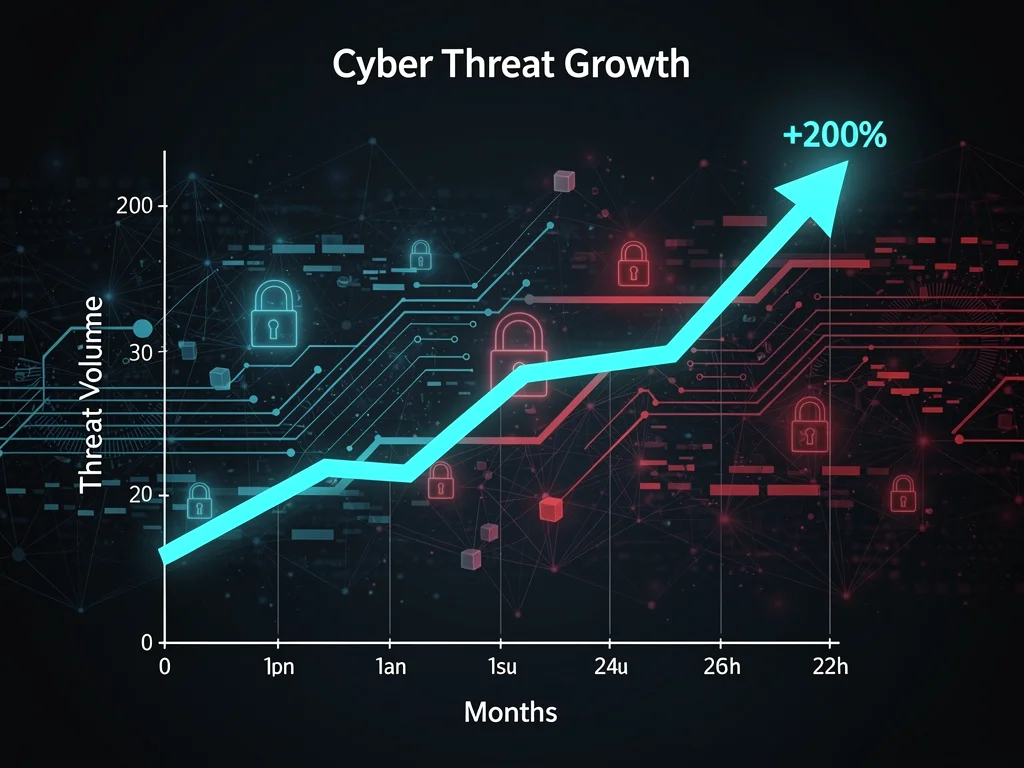
A recent report indicates a concerning 200% surge in US ransomware attacks within the last six months, underscoring the urgent need for enhanced cybersecurity measures and proactive defence strategies across all sectors.
Por: [email protected] em 10 de junho de 2026
Última atualização em: 13 de agosto de 2026
A new report has revealed a concerning 200% increase in US ransomware attacks over the past six months, signalling an urgent and escalating cybersecurity crisis impacting businesses and individuals nationwide.
A recent report has sent shockwaves through the cybersecurity community, unveiling a staggering US ransomware attacks increase of 200% within just the last six months. This alarming statistic is not merely a number; it represents a significant and growing threat to the digital infrastructure of businesses, governmental organisations, and individuals across the United States. Understanding the scope and implications of this surge is paramount for anyone operating in today’s interconnected world.
The alarming rise of ransomware in the US
The landscape of cyber threats is constantly evolving, but the recent 200% increase in US ransomware attacks marks a particularly worrying trend. This surge suggests that cybercriminals are becoming more sophisticated, audacious, and effective in their campaigns, exploiting vulnerabilities with greater precision and impact. It’s no longer a question of ‘if’ an organisation will face a ransomware attempt, but ‘when’ and ‘how prepared’ they will be.
Ransomware, a type of malicious software designed to block access to a computer system until a sum of money is paid, has historically been a significant threat. However, the current escalation indicates a fundamental shift in tactics and targets, making it a pervasive and critical issue for national security and economic stability.
Understanding the mechanics of modern ransomware
Modern ransomware attacks often begin with phishing emails, exploiting human error to gain initial access. Once inside a network, the malware spreads rapidly, encrypting critical data and demanding payment, usually in cryptocurrency, for its release. The sophistication lies not just in the encryption, but in the entire attack lifecycle, which often includes:
Initial access: Phishing, compromised credentials, or software vulnerabilities.
Lateral movement: Spreading through the network to identify and encrypt valuable assets.
Data exfiltration: Stealing sensitive data before encryption for double extortion.
Encryption and ransom demand: Locking files and demanding payment, often with a time limit.
The impact extends far beyond financial loss, encompassing reputational damage, operational downtime, and potential regulatory fines. Organisations must grasp these intricate mechanics to build robust defences.
The sheer volume of attacks highlights a critical gap in current cybersecurity defences or a growing level of vulnerability within US digital ecosystems. This section will delve into the factors contributing to this alarming rise and explore the broader implications for businesses and individuals alike. Understanding these dynamics is the first step towards effective mitigation.
Key drivers behind the 200% surge
Several interconnected factors are fuelling the dramatic 200% surge in US ransomware attacks. These drivers range from technological advancements exploited by cybercriminals to geopolitical tensions and a persistent lack of adequate cybersecurity investment across various sectors. Identifying these root causes is essential for developing targeted and effective countermeasures.
One primary driver is the increasing professionalisation of cybercrime. Ransomware-as-a-Service (RaaS) models have lowered the barrier to entry for aspiring criminals, providing them with sophisticated tools and infrastructure without requiring extensive technical expertise. This democratisation of attack capabilities has led to a proliferation of threat actors.
The rise of Ransomware-as-a-Service (RaaS)
RaaS platforms offer a complete ecosystem for launching ransomware attacks, including malware, payment processing, and even technical support. This business model has transformed ransomware into a scalable and highly profitable enterprise for criminal organisations. Affiliates pay a fee or a percentage of the ransom to the RaaS operator, making it an attractive venture with minimal overhead.
Accessibility: Low technical skill required to launch attacks.
Profitability: High returns for both operators and affiliates.
Anonymity: Cryptocurrencies and dark web infrastructure provide a layer of protection for criminals.
The ease with which these services can be accessed means that more individuals and groups are now capable of executing sophisticated attacks, contributing significantly to the overall increase.
Another significant factor is the expanding attack surface. The rapid adoption of cloud services, remote work models, and interconnected IoT devices has introduced new vulnerabilities that cybercriminals are quick to exploit. Many organisations struggle to secure these new environments effectively, leaving doors open for attackers. The COVID-19 pandemic, in particular, accelerated the shift to remote work, often without adequate security protocols in place, creating fertile ground for ransomware groups.
Furthermore, geopolitical tensions and the involvement of state-sponsored actors add another layer of complexity. While not all ransomware attacks are state-sponsored, some groups operate with tacit approval or direct support from nation-states, making them more resilient and harder to track. This backing provides them with resources and impunity that further exacerbate the threat.
The combination of professionalised cybercrime, an expanding attack surface, and geopolitical complexities creates a perfect storm, driving the unprecedented increase in ransomware incidents. Addressing these underlying issues is crucial for any long-term strategy against this pervasive threat.
The devastating impact on US businesses and infrastructure
The 200% increase in US ransomware attacks has had a profoundly devastating impact on businesses, critical infrastructure, and public services across the nation. Beyond the immediate financial demands, the long-term consequences can cripple operations, erode public trust, and even threaten national security. Understanding these multifaceted impacts is vital for grasping the true cost of this cyber scourge.
For businesses, the most immediate consequence is operational disruption. When systems are encrypted, companies face significant downtime, often leading to lost revenue, missed deadlines, and compromised customer service. This can be particularly crippling for small and medium-sized enterprises (SMEs) that may lack the resources to recover quickly.
Financial and reputational repercussions
The financial toll of ransomware attacks extends beyond the ransom payment itself. It includes the cost of incident response, forensic analysis, system restoration, legal fees, and potential regulatory fines for data breaches. Moreover, the reputational damage can be severe, leading to customer churn and a loss of market confidence. Companies that suffer attacks often face intense scrutiny and a diminished brand image.
Direct financial losses: Ransom payments, recovery costs, legal fees.
Indirect financial losses: Lost revenue during downtime, decreased productivity.
Reputational damage: Loss of customer trust, negative public perception.
The decision to pay a ransom is complex. While paying might seem like the quickest way to restore operations, it often funds future criminal activities and does not guarantee data recovery. Many victims find that even after paying, some data remains inaccessible or is leaked anyway.
Critical infrastructure, including healthcare, energy, and transportation sectors, has become an increasingly attractive target. Attacks on these sectors can have far-reaching societal consequences, disrupting essential services and potentially endangering lives. The Colonial Pipeline attack in 2021, for instance, highlighted how a single ransomware incident could cause widespread fuel shortages and panic.
The ripple effect of these attacks is also considerable. Supply chains can be disrupted when a key supplier falls victim, affecting numerous downstream businesses. This interconnectedness means that even organisations with robust defences can be indirectly impacted by an attack on a partner or vendor. The cumulative effect of these disruptions poses a significant threat to the economic stability and resilience of the United States.
In conclusion, the impact of the rising ransomware threat is pervasive and severe, affecting every facet of society. Robust defence strategies and proactive measures are no longer optional but are critical imperatives for survival in the current digital age.
Government and industry response efforts
In response to the escalating threat of US ransomware attacks, both government agencies and private industry have intensified their efforts to combat cybercrime. These responses encompass a range of initiatives, from enhanced intelligence sharing and law enforcement operations to the development of new cybersecurity frameworks and public awareness campaigns. A coordinated, multi-faceted approach is essential to turn the tide against these persistent threats.
Government agencies, such as the Cybersecurity and Infrastructure Security Agency (CISA), the FBI, and the National Institute of Standards and Technology (NIST), are at the forefront of these efforts. CISA, for example, provides resources and guidance to organisations to help them improve their cyber hygiene and resilience against ransomware.
Collaborative defence initiatives
Collaboration between government and industry is crucial. Information sharing partnerships allow for the rapid dissemination of threat intelligence, enabling organisations to proactively defend against emerging attack vectors. Joint task forces are also being established to investigate and disrupt ransomware operations.
Threat intelligence sharing: Rapid dissemination of attack indicators and tactics.
Law enforcement actions: Disrupting criminal infrastructure and arresting perpetrators.
Public-private partnerships: Fostering collaboration for collective defence.
The US government has also taken a more aggressive stance, imposing sanctions on individuals and entities involved in ransomware activities and actively pursuing the recovery of stolen funds. These actions aim to deter cybercriminals and diminish the profitability of their operations.
From the industry side, there’s a growing emphasis on adopting advanced security solutions, implementing zero-trust architectures, and investing in employee training. Cybersecurity vendors are continuously innovating, offering new tools for endpoint detection and response (EDR), extended detection and response (XDR), and Security Information and Event Management (SIEM) systems to help organisations detect and respond to threats more effectively.
Furthermore, cybersecurity insurance is becoming a more common component of risk management strategies, though insurers are also raising their requirements for coverage due to the increased frequency and severity of attacks. This creates an incentive for organisations to improve their security posture to qualify for and afford insurance.
Despite these significant efforts, the battle against ransomware is ongoing. The adaptability of cybercriminals means that defence strategies must also evolve constantly, requiring continuous investment and innovation from both the public and private sectors.
Essential strategies for ransomware prevention
Given the alarming 200% increase in US ransomware attacks, implementing robust prevention strategies is no longer optional but a fundamental requirement for any organisation. A multi-layered approach, combining technical controls with human awareness, is the most effective way to mitigate the risk of falling victim to these pervasive threats. Proactive defence is always more cost-effective than reactive recovery.
The foundation of any strong cybersecurity posture begins with basic cyber hygiene. Many ransomware attacks succeed by exploiting common vulnerabilities that could be easily addressed through diligent practices. This includes regular software updates and robust patch management to close known security gaps.
Implementing a multi-layered security approach
A comprehensive defence strategy involves several critical components working in concert. No single solution can guarantee absolute protection, but a combination of measures significantly reduces the attack surface and increases resilience.
Regular data backups: Ensure critical data is backed up regularly, offline, and tested for restorability.
Endpoint detection and response (EDR): Advanced tools to monitor and respond to threats on devices.
Network segmentation: Isolate critical systems to prevent lateral movement of malware.
Email filtering and anti-phishing training: Reduce the risk of initial compromise through social engineering.
Multi-factor authentication (MFA): Add an extra layer of security to user accounts.
Beyond technical controls, employee training is paramount. The human element remains the weakest link in many security chains. Regular, engaging training sessions can empower employees to identify phishing attempts, recognise suspicious behaviour, and follow security protocols diligently. A security-aware workforce is a powerful line of defence.
Organisations should also develop and regularly test an incident response plan. Knowing exactly what steps to take during and after an attack can significantly reduce downtime and the overall impact. This plan should include clear roles and responsibilities, communication protocols, and procedures for data recovery.
Furthermore, adopting a zero-trust security model, where no user or device is inherently trusted, regardless of their location, can dramatically enhance security. This approach requires continuous verification of identity and access, limiting the potential damage if an attacker gains initial access.
By integrating these essential strategies, organisations can build a resilient defence against the ever-present threat of ransomware, protecting their assets and ensuring business continuity.
The future of ransomware and cybersecurity
The future trajectory of ransomware and cybersecurity is one of continuous evolution, with both attackers and defenders constantly adapting their tactics. The recent 200% increase in US ransomware attacks is a stark reminder that the threat is not diminishing but transforming. Anticipating these changes is critical for developing future-proof defence strategies and staying ahead of cybercriminals.
One emerging trend is the increasing use of artificial intelligence (AI) and machine learning (ML) by both sides. Cybercriminals are beginning to leverage AI to craft more convincing phishing attacks, automate reconnaissance, and evade detection. Conversely, defenders are using AI/ML to enhance threat detection, automate incident response, and identify anomalies in network behaviour.
Emerging threats and defensive innovations
The sophistication of ransomware attacks is expected to grow, with more targeted campaigns focusing on specific industries or high-value organisations. Double and triple extortion tactics, where data is exfiltrated, encrypted, and then used to pressure multiple parties (e.g., the victim, their customers, or suppliers), will likely become more prevalent.
AI-driven attacks: More sophisticated and evasive malware.
Supply chain attacks: Targeting vulnerabilities in third-party vendors.
New extortion models: Beyond data encryption, including DDoS and reputational damage.
Quantum computing threats: Potential to break current encryption standards in the long term.
Another area of concern is the increasing focus on critical infrastructure and operational technology (OT) systems. As these systems become more connected to IT networks, they present new targets for ransomware, with potentially catastrophic consequences for society.
On the defensive front, organisations will need to embrace more proactive and predictive security measures. This includes greater investment in threat intelligence, security orchestration, automation, and response (SOAR) platforms, and a shift towards security by design principles, embedding security considerations from the outset of system development.
The cybersecurity workforce shortage also remains a significant challenge. Addressing this gap through education, training, and talent development programmes will be crucial for building a resilient national defence against future cyber threats. International cooperation will also play a vital role in combating cross-border cybercrime and dismantling criminal networks.
Ultimately, the future of cybersecurity will be defined by an ongoing arms race. Organisations and governments must remain vigilant, adaptable, and committed to continuous improvement to protect against the evolving landscape of ransomware threats.
Legal and ethical considerations of ransomware
The escalating 200% increase in US ransomware attacks brings to the forefront a complex web of legal and ethical considerations that organisations and policymakers must navigate. These issues range from the legality of paying ransoms to the ethical responsibilities of reporting breaches and protecting victim data. A clear understanding of these dimensions is crucial for responsible and effective incident management.
One of the most contentious issues is whether to pay the ransom. While law enforcement agencies generally advise against it, arguing that it funds criminal enterprises, many organisations feel compelled to pay to restore critical operations and avoid severe business disruption. This dilemma creates a moral and practical challenge for victims.
The debate over ransom payments
Paying a ransom does not guarantee data recovery, nor does it prevent future attacks. In some cases, organisations that pay are targeted again. Furthermore, in certain circumstances, paying a ransom could inadvertently violate sanctions laws if the payment goes to a sanctioned entity or individual.
Legal implications: Potential violation of sanctions, funding criminal activity.
Ethical dilemma: Balancing business continuity with supporting criminals.
Effectiveness: No guarantee of data recovery or prevention of future attacks.
The ethical implications extend to data privacy and notification requirements. When a ransomware attack results in a data breach, organisations have a legal and ethical obligation to inform affected individuals and regulatory bodies. This process can be complex, especially with varying state and federal laws.
The legal landscape surrounding ransomware is also evolving. Governments are exploring new legislation to deter attacks, enhance reporting requirements, and potentially regulate ransom payments. However, balancing these measures with the need for organisations to recover quickly is a delicate act.
Another ethical consideration involves the sharing of threat intelligence. While sharing information can aid in collective defence, it also raises concerns about privacy and proprietary data. Striking the right balance between collaboration and confidentiality is a continuous challenge in the cybersecurity community.
Ultimately, the legal and ethical framework for ransomware is still being developed. Organisations must stay informed of legal requirements, consult with legal counsel, and develop clear internal policies regarding ransom payments and breach reporting to navigate this complex terrain responsibly.
Building cyber resilience in a hostile environment
In light of the staggering 200% increase in US ransomware attacks, building robust cyber resilience has become an absolute imperative for every organisation, regardless of size or sector. Resilience goes beyond mere prevention; it encompasses the ability to withstand, respond to, and recover from cyberattacks effectively, minimising disruption and ensuring business continuity in an increasingly hostile digital environment.
A key component of cyber resilience is developing a comprehensive incident response plan. This plan should be well-documented, regularly updated, and frequently tested through simulations and tabletop exercises. Knowing precisely what to do when an attack occurs can dramatically reduce recovery times and overall impact.
Key pillars of a resilient cybersecurity framework
True cyber resilience is built upon several foundational pillars that address different aspects of an organisation’s security posture. These pillars work together to create a robust defence-in-depth strategy.
Proactive risk management: Continuous assessment of vulnerabilities and threats.
Robust backup and recovery: Immutable backups and well-tested restoration procedures.
Employee training and awareness: Cultivating a security-conscious culture.
Adaptive security technologies: Implementing AI/ML-driven detection and response tools.
Third-party risk management: Securing the supply chain and vendor ecosystem.
Continuous monitoring and threat intelligence are also critical. Organisations need to have visibility into their networks and systems to detect anomalous behaviour early. Leveraging threat intelligence feeds can help anticipate new attack vectors and strengthen defences proactively.
Furthermore, fostering a culture of security throughout the organisation is vital. Cybersecurity should not be viewed solely as an IT department responsibility but as a collective effort involving every employee. Leadership commitment and regular communication about security best practices are essential for embedding this culture.
Partnerships with cybersecurity experts, including managed security service providers (MSSPs) and incident response firms, can provide valuable external support and expertise, especially for organisations with limited internal resources. These partnerships can offer access to advanced tools, skilled personnel, and up-to-date threat intelligence.
In conclusion, building cyber resilience is an ongoing journey that requires continuous investment, adaptation, and collaboration. By focusing on these key pillars, organisations can not only protect themselves from the immediate threat of ransomware but also build a more secure and sustainable digital future.
Key Aspect
Brief Description
Ransomware Surge
US ransomware attacks increased by 200% in six months, posing a critical threat.
Key Drivers
Professionalisation of cybercrime (RaaS), expanding attack surfaces, and geopolitical factors.
Impact
Devastating financial losses, operational disruption, and reputational damage for businesses and infrastructure.
Prevention
Multi-layered security, regular backups, employee training, and incident response planning are essential.
Frequently asked questions about ransomware
What is ransomware and how does it work?▼
Ransomware is malicious software that encrypts a victim’s files, blocking access until a ransom is paid, typically in cryptocurrency. Attackers usually gain access through phishing emails or exploiting software vulnerabilities, then spread through networks, encrypting valuable data and threatening its permanent loss or public release if payment is withheld.
Why have US ransomware attacks increased by 200%?▼
The 200% increase is attributed to several factors, including the proliferation of Ransomware-as-a-Service (RaaS) models, which lower the barrier to entry for cybercriminals. Additionally, expanding attack surfaces due to remote work and cloud adoption, coupled with geopolitical tensions, contribute to the heightened threat landscape across the US.
What are the main consequences of a ransomware attack?▼
The consequences are severe, including significant financial losses from ransom payments, recovery costs, and operational downtime. Attacks also lead to reputational damage, loss of customer trust, and potential legal or regulatory fines. For critical infrastructure, disruptions can affect essential services and public safety.
What steps can organisations take to prevent ransomware?▼
Effective prevention involves a multi-layered approach: regular data backups (offline), robust patch management, multi-factor authentication (MFA), strong email filtering, employee cybersecurity training, and implementing endpoint detection and response (EDR) solutions. An updated incident response plan is also crucial for quick recovery.
Should organisations pay the ransom if attacked?▼
Law enforcement generally advises against paying ransoms as it funds criminal activities and offers no guarantee of data recovery. Paying can also lead to re-targeting. Organisations must weigh the legal implications, ethical considerations, and potential business impact, often consulting with cybersecurity experts and legal counsel before making a decision.
Conclusion
The alarming 200% increase in US ransomware attacks over the past six months serves as a critical wake-up call for every sector and individual. This unprecedented surge underscores the urgent need for enhanced vigilance, robust cybersecurity investments, and a collective commitment to cyber resilience. As cybercriminals grow more sophisticated, exploiting new vulnerabilities and leveraging advanced tactics like Ransomware-as-a-Service, the onus is on organisations to adopt comprehensive, multi-layered defence strategies. From implementing strong technical controls and regular data backups to fostering a security-aware culture through continuous employee training and developing well-tested incident response plans, proactive measures are paramount. The fight against ransomware is an ongoing battle, demanding constant adaptation, collaboration between government and industry, and a forward-thinking approach to protect our digital infrastructure and ensure a secure future.
I'm a journalist with a passion for creating engaging content. My goal is to empower readers with the knowledge they need to make informed decisions and achieve their goals.